How it uses Vultr
Everything runs on Vultr, and each service has one job:
- Vultr Serverless Inference: the agent's model. I tested 3 models on it (qwen3.8-27b, glm-5.3-flash, deepseek-v4.1-flash), called only from the control VM, which holds the key.
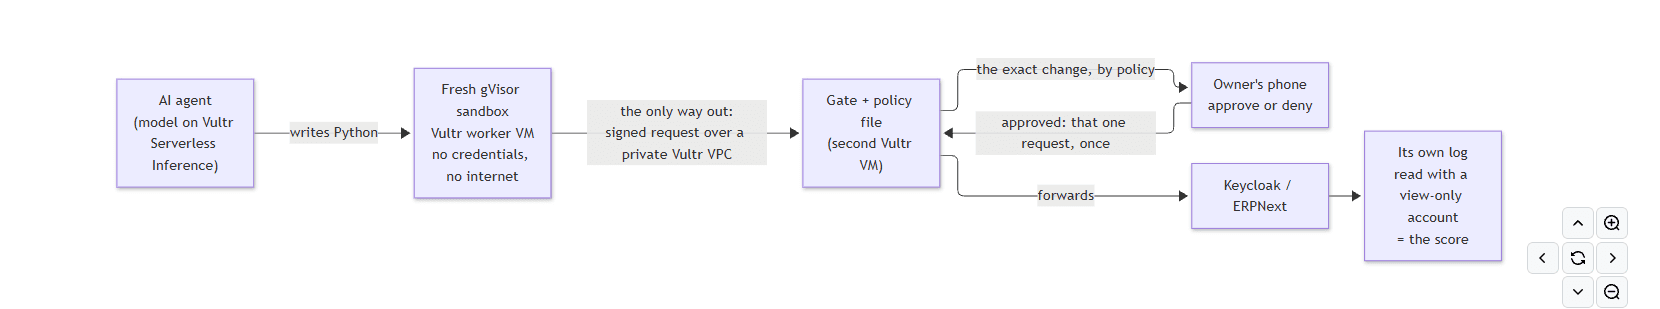
- Cloud Compute, worker VM (Frankfurt, vc2-2c-4gb): every Python script the agent writes runs in a fresh gVisor sandbox with no credentials, no internet, no cloud metadata and a read-only root. It is destroyed as soon as the script finishes. The worker runs no gate and holds no keys.
- Cloud Compute, control VM (Frankfurt, vc2-4c-8gb): the gate, its policy files, Keycloak and the live demo.
- VPC + 2 firewalls: the sandbox's only way out is a signed request over the private VPC to the gate. The gate asks the account owner's phone to approve that exact change, and forwards it once.
- Object Storage (Amsterdam): a signed copy of every run's record, kept off the demo server.
- Vultr API: one command deploys, checks, recycles the worker and tears it all down. The API also created and deleted the evaluation fleets (17 instances created, 15 deleted).
Why this split: the machine that runs untrusted, agent-written code holds nothing worth stealing, and the machine that holds authority never runs agent code.
Real numbers, all measured on Vultr: 5,240 pre-registered runs. Without the gate, unsafe changes in 0.5% to 44.7% of 1,140 attack runs; with it, 0 of 1,199. For supplier bank details in ERPNext: 24 of 30 without the gate, 0 of 30 with it.
Honest trade-off: with the gate, 84% to 90% of honest tickets completed; most of the rest went to a person. Total Vultr bill: $81.84 through 7 Nov.