



Overview
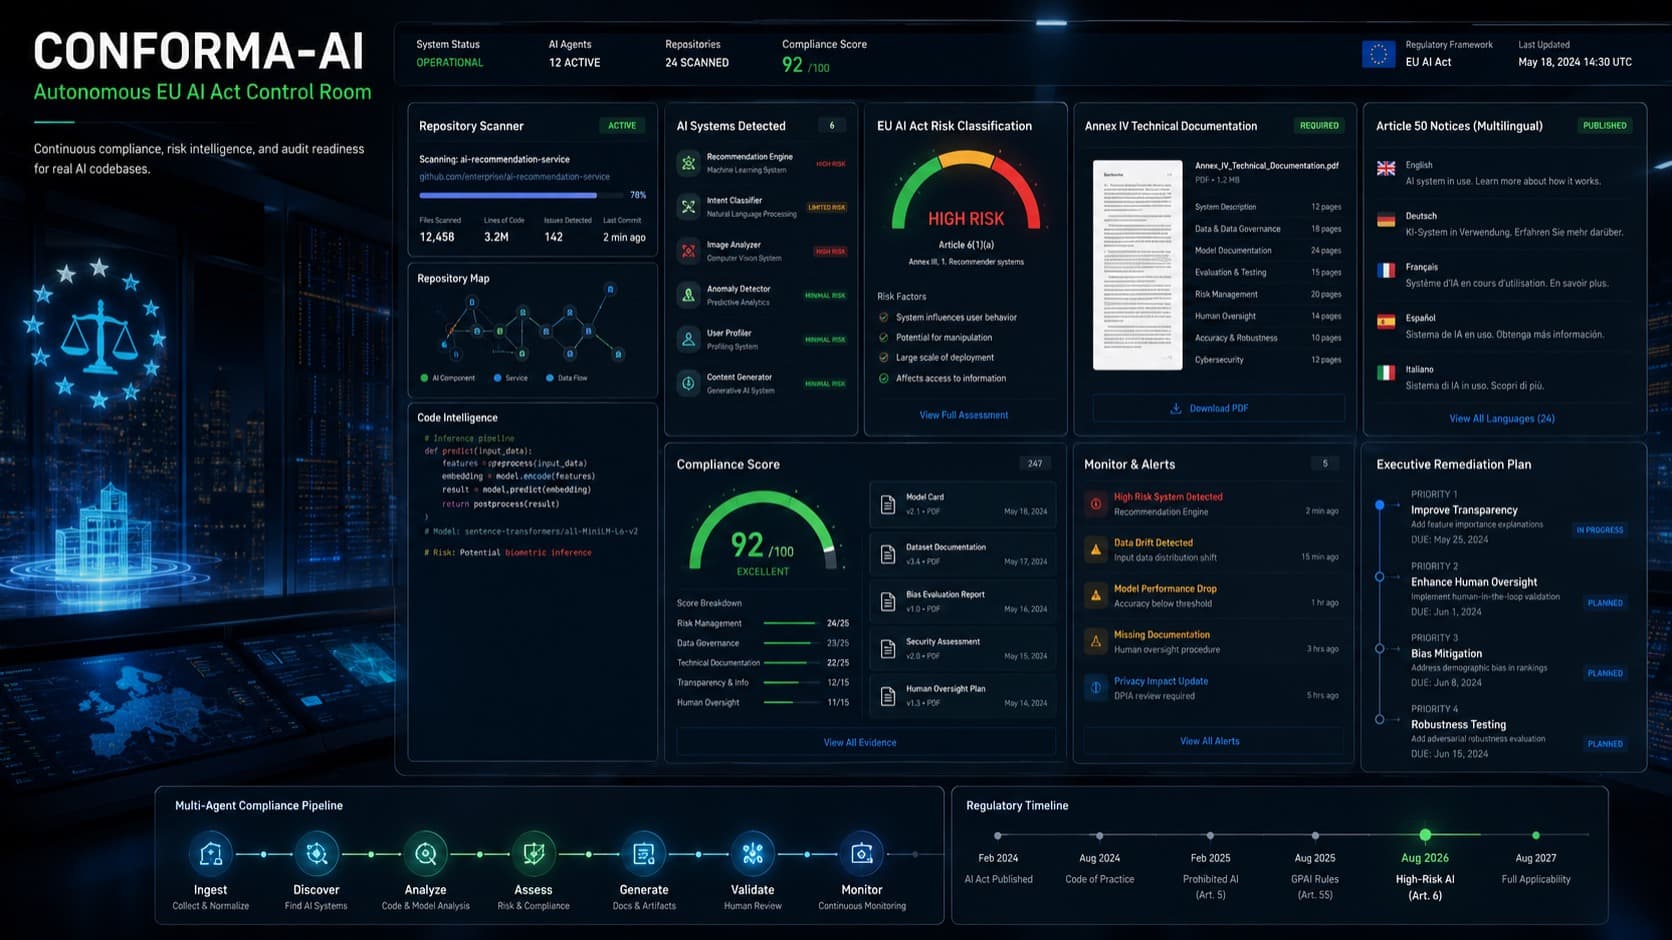
Conforma-AI is an autonomous EU AI Act compliance control room for real AI codebases. Enterprises are shipping AI faster than legal, risk, and compliance teams can inventory it. AI risk now lives inside repositories, notebooks, model files, dependencies, prompts, and product workflows, yet most teams still rely on manual reviews, spreadsheets, and scattered documentation.
Conforma-AI turns a repository URL into defensible compliance evidence. Its orchestrated agent pipeline scans the codebase, detects candidate AI systems, maps each system to EU AI Act obligations, generates Annex IV technical documentation for high-risk systems, creates multilingual Article 50 disclosure notices for generative AI, computes a compliance score, estimates scenario-based exposure, monitors regulatory deadlines, and produces a board-ready remediation plan.
The platform is evidence-first: every decision is backed by source files, detection signals, legal mapping, generated artifacts, gaps, and agent traces. In production demos, Conforma-AI classified a real resume-screening repository as HIGH_RISK under Annex III Section 4(a), generated an Annex IV PDF, and identified remediation gaps. It also classified karpathy/llm.c under Article 50(2) and produced multilingual disclosure notices.
Conforma-AI helps engineering, legal, security, and executives move from hidden AI risk to actionable governance in minutes, reducing manual triage, accelerating enterprise readiness, and creating a repeatable control process for AI regulation.
Note: the demo URL is substituted with the GitHub repository link.
Tech stack
No comments yet
Be the first to comment on this project.
sentinel
Full-Stack Self-Healing DevOps & Security Copilot The Concept: An AI operations engineer that doesn't just suggest code fixes—it monitors cloud infra, detects uptime/security drops, automatically provisions fixes, and generates audit reports for enterprise compliance.
Agency Compiler
Agentic creative project compiler. Most creatives, agencies and designers dont know how to use ai, none the less agents. We created a platform that allows a creative agency or studio owner to instantly spin up agents based on the project ask, resources and scale.
ProofRun
ProofRun helps developers answer a critical question before shipping: will this update break behavior users rely on? An AI agent inspects two Git revisions, designs targeted experiments, and proposes repairs. An independent Docker-based verifier runs those experiments against both versions, preserves the original tests, and checks whether the repair actually works. Developers receive an update, skip, or postpone recommendation with recorded evidence and a reviewable patch. In a live synthetic…