



Overview
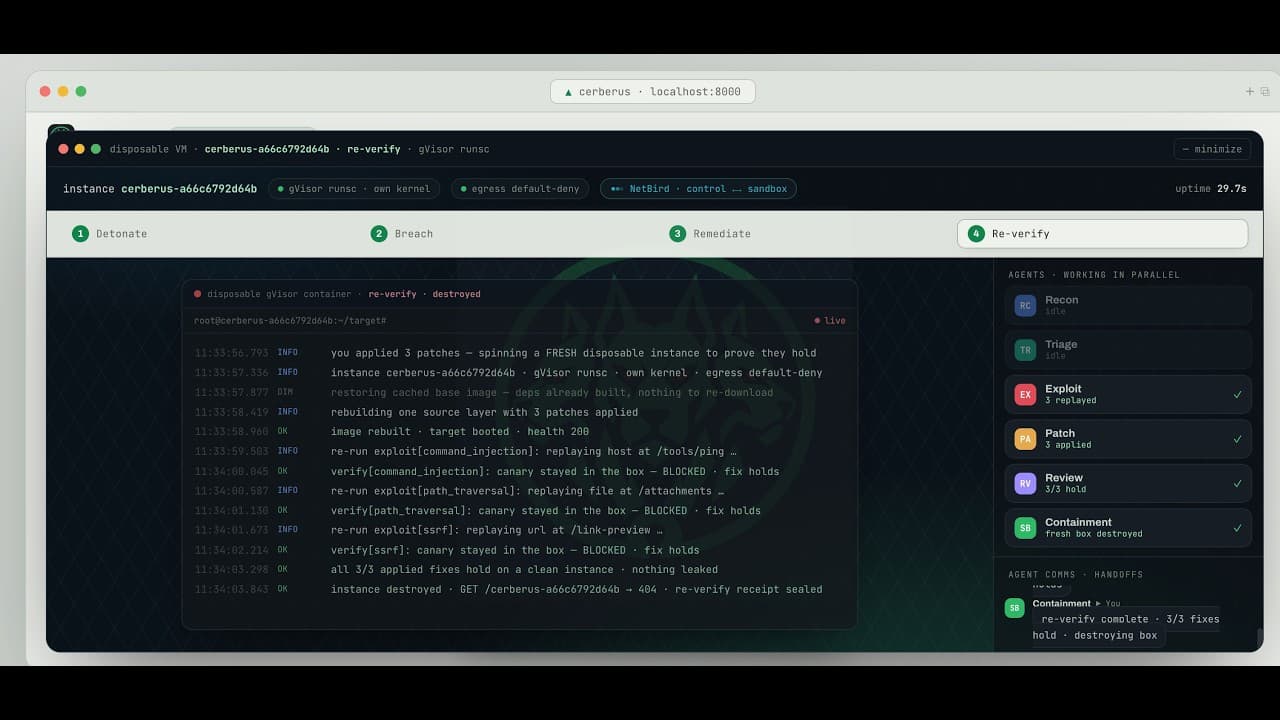
Cerberus: evidence backed repo verification on throwaway Vultr VX1s. You hand it a repo. It clones it read-only, then boots it on a disposable VX1 in your private Vultr VPC. Your code runs inside gVisor or a KVM microVM (Microsandbox), never on the control host. It lands real exploits (SQLi, path traversal, command injection, SSRF, auth bypass), but only counts a finding when a canary secret actually leaves the box; the environment decides, not the model. Then it patches the code, reproves each fix on a second throwaway VX1, and certifies closed only when the exploit fails while a legitimate request still works. Inference triage runs on Vultr Serverless Inference. All evidence flows over the VPC. The sandbox is destroyed, with the provider's 404 proving cleanup. Proven live on five vulnerability classes; the demo web tier is password-gated.
Note: the demo URL is substituted with the GitHub repository link.
Tech stack
No comments yet
Be the first to comment on this project.
sentinel
Full-Stack Self-Healing DevOps & Security Copilot The Concept: An AI operations engineer that doesn't just suggest code fixes—it monitors cloud infra, detects uptime/security drops, automatically provisions fixes, and generates audit reports for enterprise compliance.
Agency Compiler
Agentic creative project compiler. Most creatives, agencies and designers dont know how to use ai, none the less agents. We created a platform that allows a creative agency or studio owner to instantly spin up agents based on the project ask, resources and scale.
ProofRun
ProofRun helps developers answer a critical question before shipping: will this update break behavior users rely on? An AI agent inspects two Git revisions, designs targeted experiments, and proposes repairs. An independent Docker-based verifier runs those experiments against both versions, preserves the original tests, and checks whether the repair actually works. Developers receive an update, skip, or postpone recommendation with recorded evidence and a reviewable patch. In a live synthetic…