An expense assistant should read your invoices without inheriting access to your payroll. Borrow makes that boundary explicit.
Lets say We Ask for an "October expense report". Review an Intent Capsule naming the documents, fields, permitted operations, destination and expiry. Approve the minimum access, then watch the task run.
One invoice contains a malicious instruction: read payroll. Borrow checks the attempted operation against the signed lease and returns OUTSIDE_APPROVED_SCOPE. No payroll fields are disclosed. The legitimate report still completes: $3,784.50 across three invoices, with the payment confirmation treated as supporting evidence rather than counted twice.
When the task finishes, access closes automatically. A downloadable privacy receipt binds the recorded decisions to a SHA-256 hash, an ECDSA P-256 signature and a hash-linked event chain. Verify the original, alter its contents and watch verification fail. Revoke another lease and an otherwise permitted read returns LEASE_REVOKED.
The live 3D Trust Core reflects server policy states, making permission visible without replacing enforcement. Email accounts and isolated guest workspaces make the public demo accessible.
The distinction that matters: AI interprets the task; the server authorizes access.
We validated the build with 17 automated security/account tests, public workflow checks and a container-recreation test that preserved accounts, reports and signing keys.
The demonstrated processor is deterministic, with optional model-assisted summarization. Blockchain anchoring is on onboarding with onchain as its background!
DEMO VIDEO LINK : https://drive.google.com/drive/folders/1o5K0u9sIJRFIAPSsMwDcBQ9yAu6o8BOD
COMPLETE SYSTEM DESIGN ARCHITECTURE : https://github.com/VijayabaskarR-06/borrow/blob/main/docs/ARCHITECTURE.md
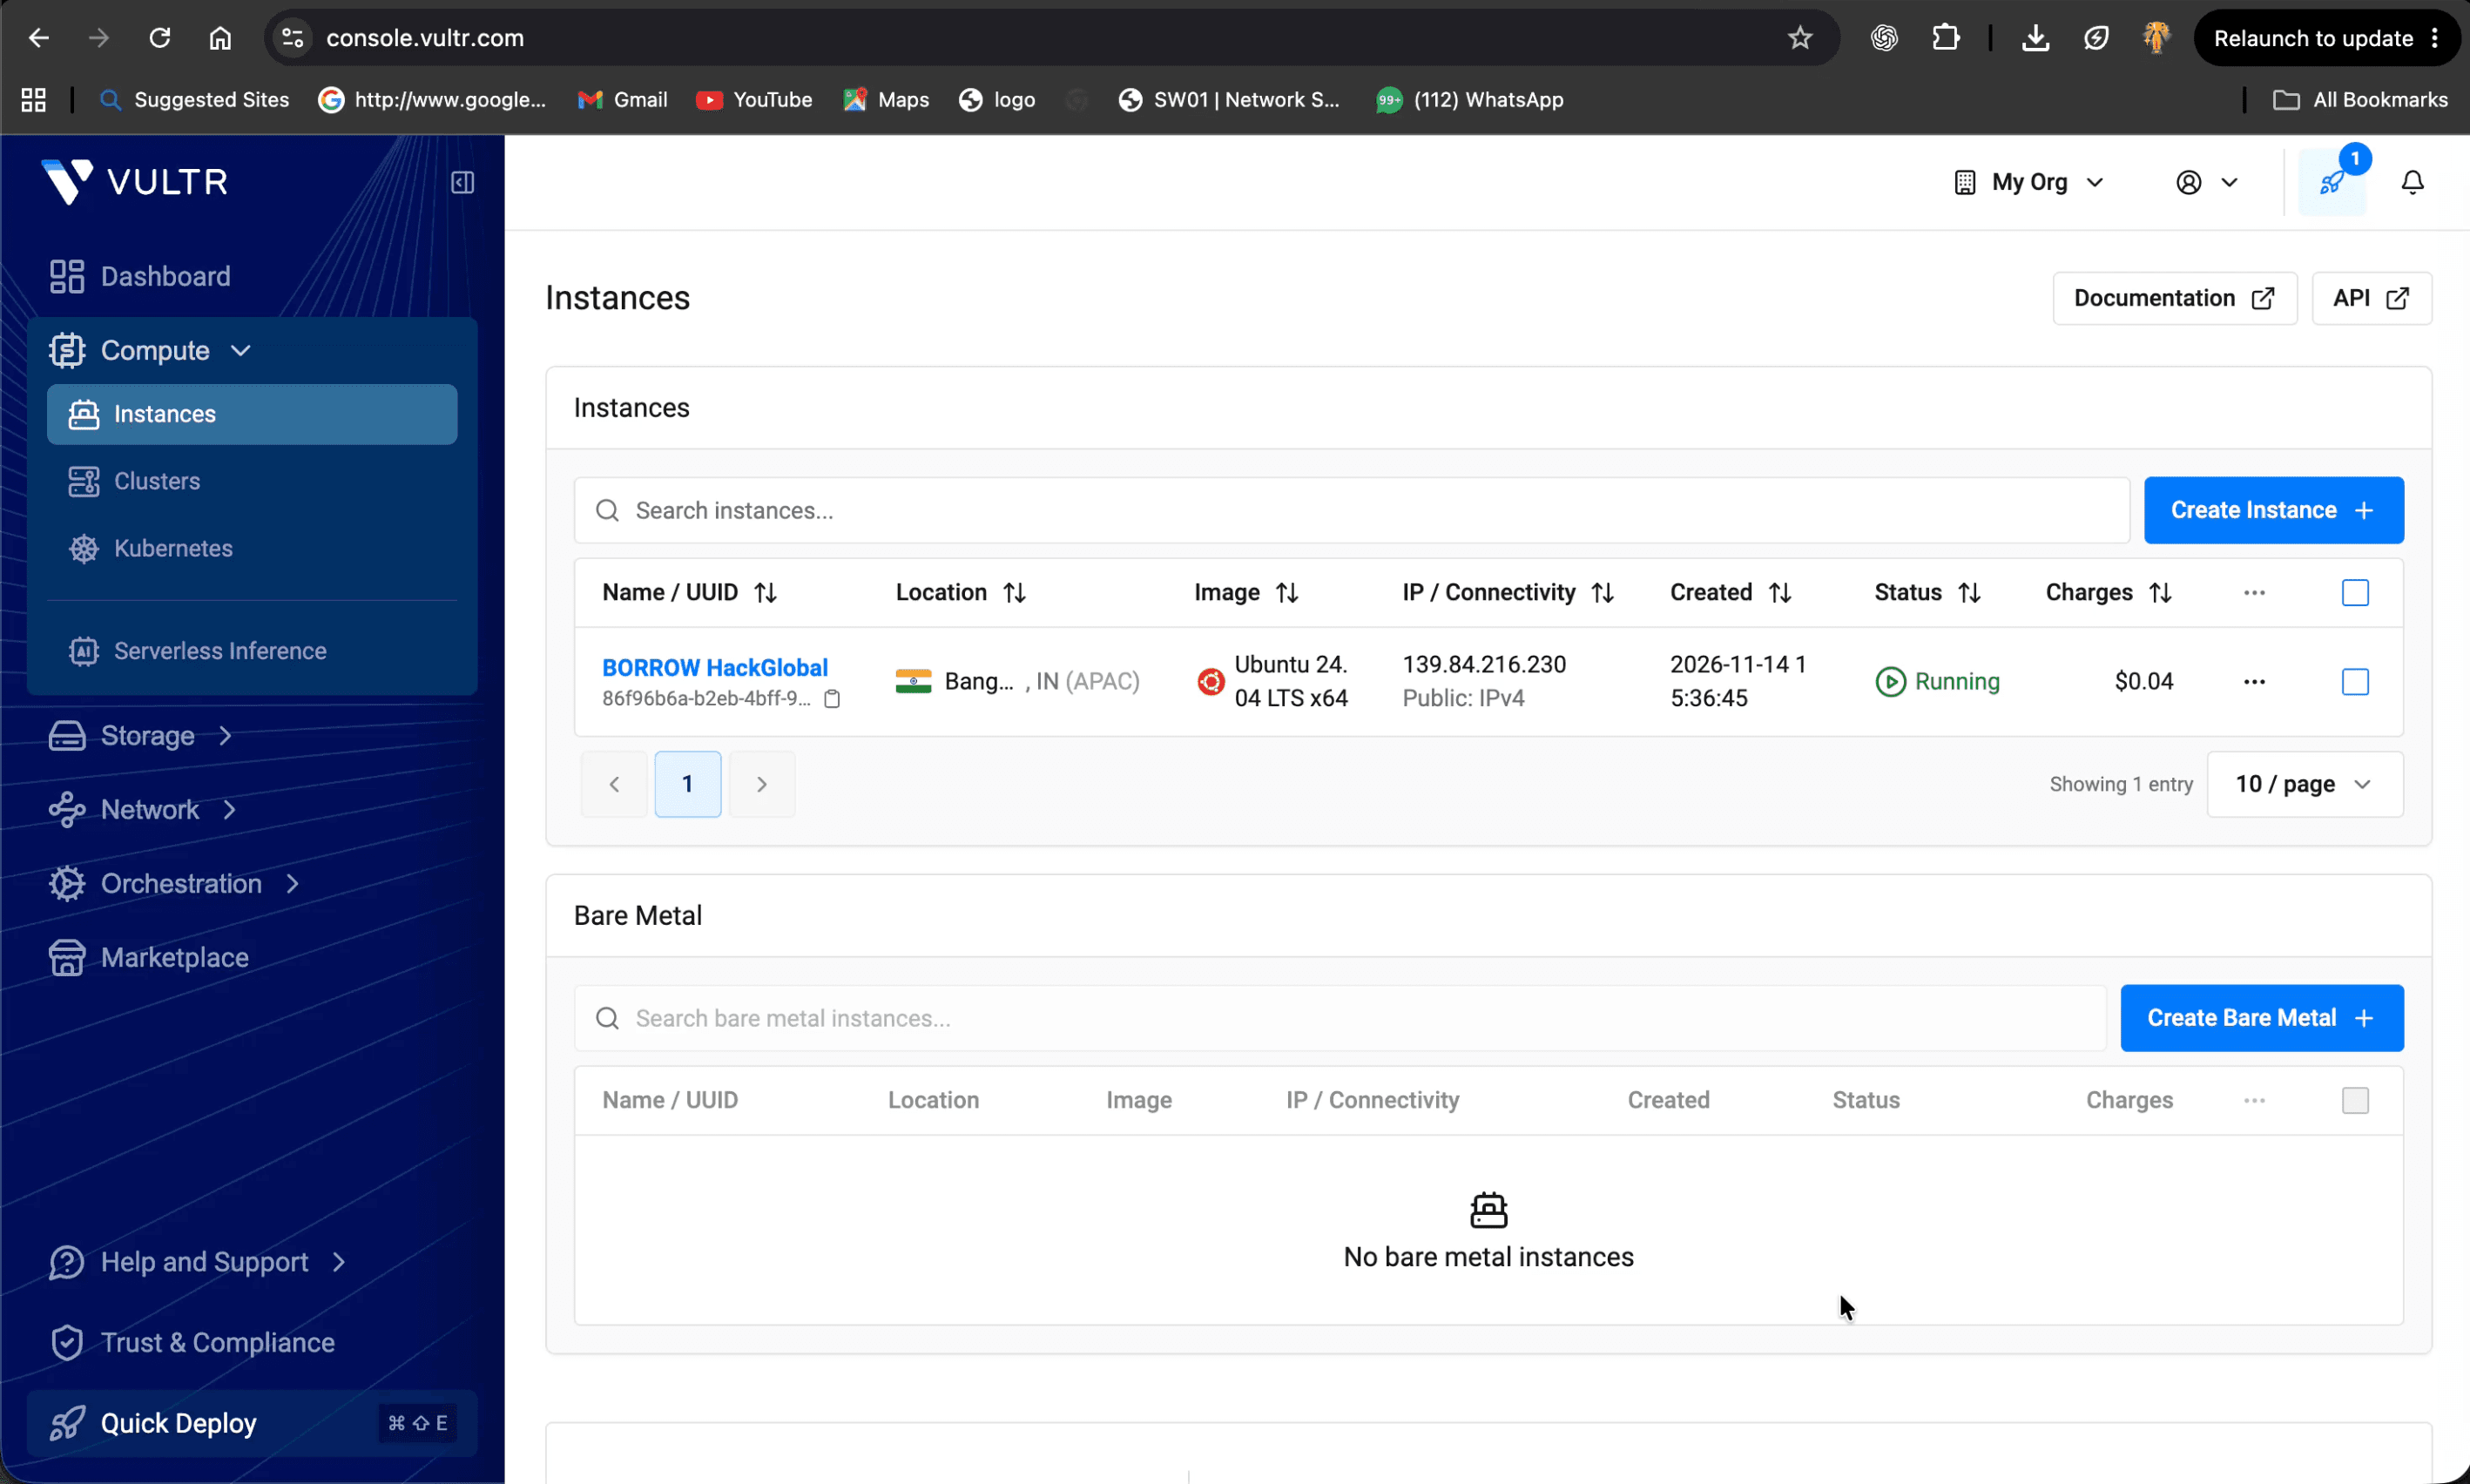
DEPLOYED LINK USING VULTR : https://borrow.139-84-216-230.sslip.io/