AegisBox: Blast Radius Zero Sandboxed Execution Agent on Vultr

AegisBox is an execution engine that lets AI agents write and run code but forces that execution into a strictly contained, air-gapped environment with zero blast radius. It transforms dangerous, unrestricted agent execution into safe, verifiable, enterprise-grade compute.

Live demoGitHub0

Overview

AegisBox is a containment-first autonomous execution agent designed for Vultr Challenge 1: Blast Radius Zero.

Key Architecture:

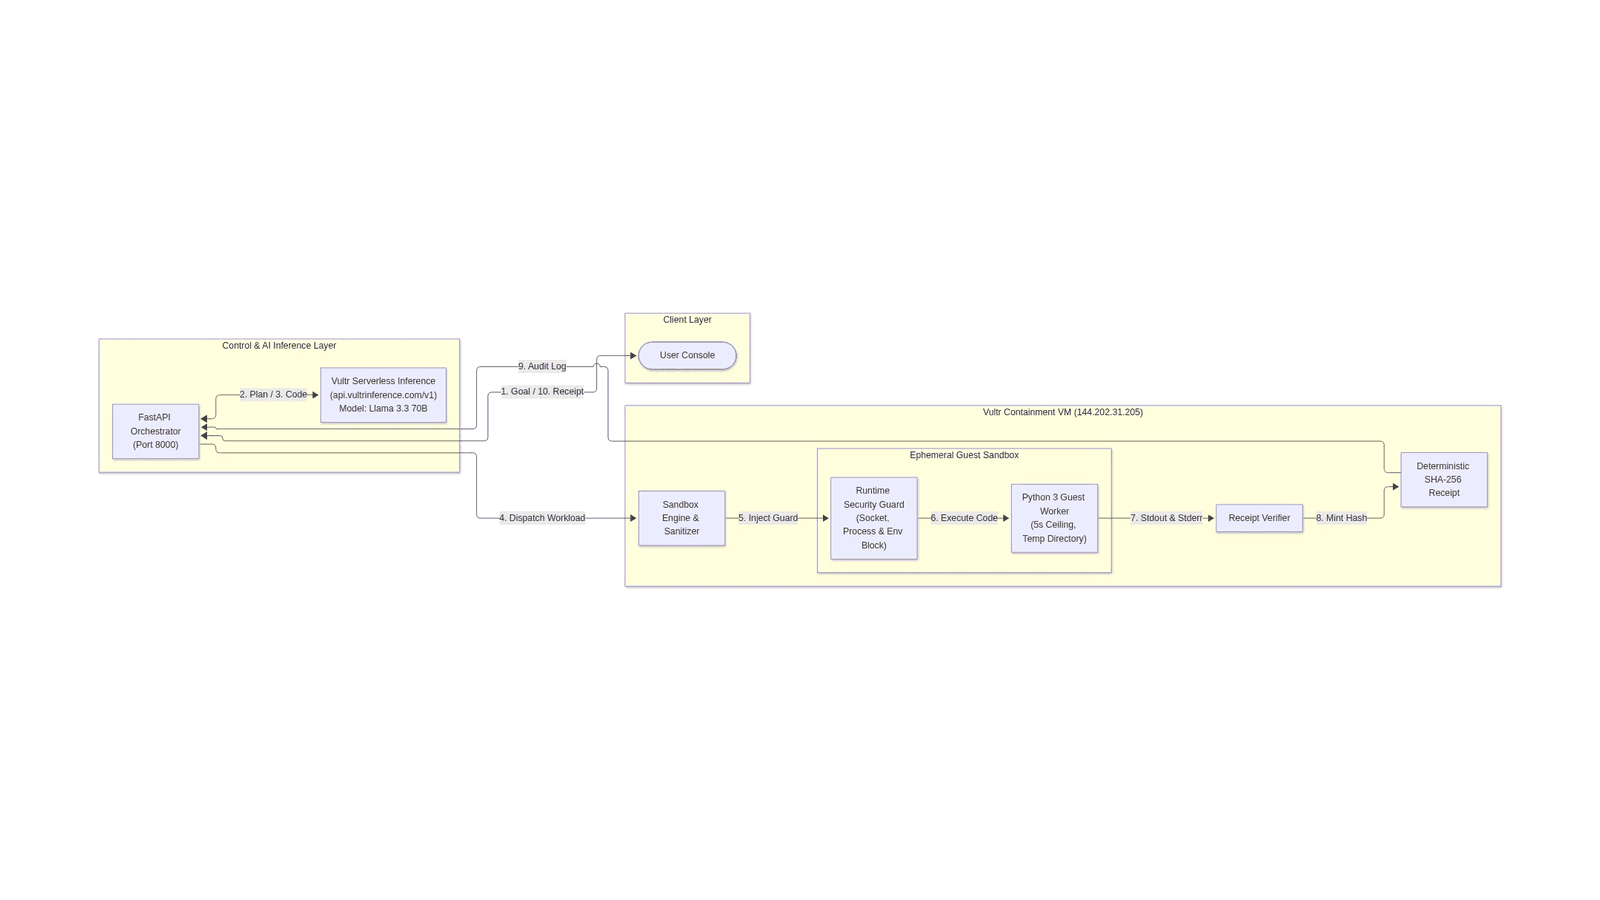
- Plans multi-step execution tasks using Vultr Serverless Inference (meta/llama-3.3-70b-instruct).

- Dispatches untrusted code into ephemeral, unprivileged sandboxes hosted on a Vultr Cloud Compute VM (IP: 144.202.31.205).

- Enforces strict secret hygiene: host environment variables and Vultr API keys are completely isolated from the execution runtime.

- Mints deterministic SHA-256 cryptographic receipts for every run.

- Demonstrates active containment moments by intercepting unauthorized network egress and system reconnaissance.

GitHub: https://github.com/Modeste01/aegisbox

The architecture screenshot is at: https://github.com/Modeste01/aegisbox/blob/master/architecture_diagram.png

Tech Stack:

• Cloud Host: Vultr Cloud Compute (Ubuntu 24.04 VM at 144.202.31.205)

• AI & LLM: Vultr Serverless Inference (api.vultrinference.com/v1, Meta Llama 3.3 70B)

• Backend: Python 3, FastAPI, Uvicorn, Pydantic

• Sandbox & Containment: Ephemeral workspace isolation, runtime socket air-gap, 5s watchdog ceiling

• Verification: Cryptographic SHA-256 receipt minting

• Frontend: Responsive Web Console (HTML5, Tailwind CSS, JetBrains Mono)

• Deployment: Docker & Docker Compose

How it uses Vultr

Vultr serves as the entire end-to-end backbone of AegisBox across compute and serverless AI: 1. Vultr Serverless Inference (api.vultrinference.com/v1): Powers the agent's cognitive layer. Every task goal entered by the user is routed to Vultr-hosted open-source models (meta/llama-3.3-70b-instruct) to formulate multi-step plans and generate isolated execution code. 2. Vultr Cloud Compute (Standard VM in Atlanta, US): Hosts the centralized FastAPI control plane and orchestrates ephemeral, throwaway sandbox environments where untrusted code is executed with strict memory, process, and network boundaries. 3. Infrastructure Containment: Rather than running code on client machines or unsecured containers, Vultr provides the isolated cloud runtime where rogue actions (such as attempted key extraction or socket egress) are intercepted, neutralized, and audited with deterministic SHA-256 execution receipts.

No comments yet

Be the first to comment on this project.